Trackline
Ticket tracker
A team ticket tracker with subtasks, notes, watchers, linked tickets and the emails it sends.
- Next.js 16
- React 19
- TypeScript
- PostgreSQL
- Files
- 54
- Lines
- 6,345
- Source
- ₹12,499
Privacy and consent for India's DPDP Act and Rules: a notice in English and Indian languages, a consent banner and form (a parent's email code for under-18s), a receipt for every answer, a privacy page where people withdraw consent or ask to see, correct or erase their data, requests with deadlines, a 72-hour breach register, and a data map with vendors.
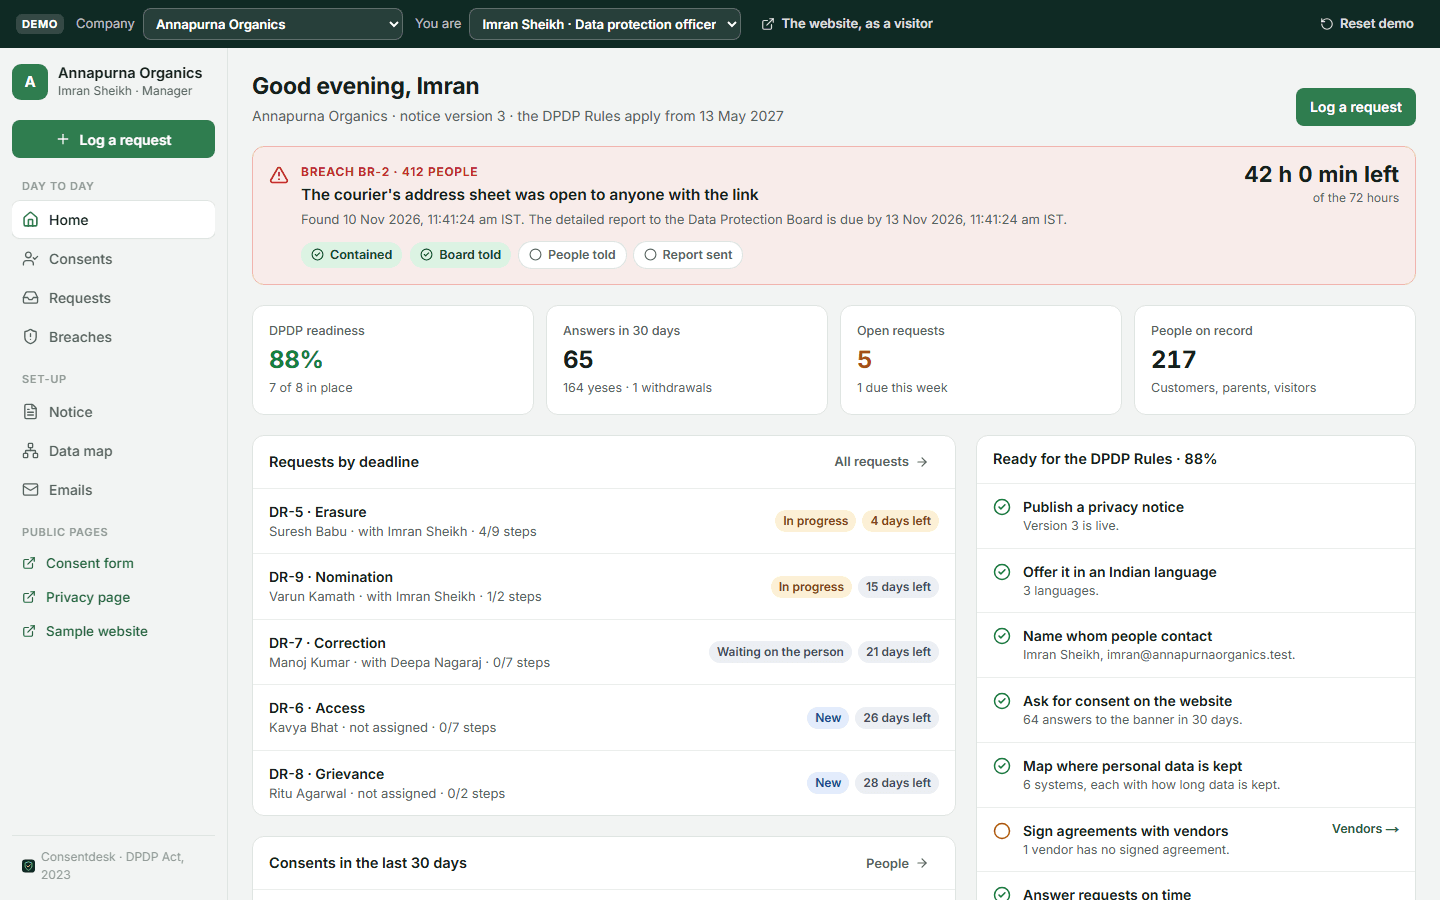
Home: readiness, deadlines and the 72-hour clock
1 / 6
Online shops, clinics and service businesses
A banner and a form that take consent the way the Rules expect, receipts you can show, and a privacy page that answers customers before they need to complain.
Schools, coaching centres and children's apps
Under-18s need a parent's verifiable consent: the parent confirms with a code sent to their email, one parent can give consent for each child, and every answer is on record.
CA firms, consultants and agencies
Run a separate company per client from one installation: their notice, banner, requests and breach register, with a readiness score to show progress before May 2027.
Live now
Try it before you download it. Annapurna Organics, an online grocery in Bengaluru, after four months of website visitors answering the banner, customers consenting at checkout, a few withdrawing, and nine requests. Its courier's breach is on Home with the 72-hour clock running. Open the website as a visitor, the consent form, or the privacy page (the code that would be emailed is shown). A school in Mysuru, with parents giving consent for their children, is one switch away. No sign-up.
Home
Readiness, a breach's 72-hour clock, requests by deadline, consents in 30 days.
Open homeRequests
Erasure, access, correction, a complaint and a nomination, each with its deadline and checklist.
Open requestsBreaches
The courier's open breach with its steps and the drafts for the Board.
Open breachesConsents
Everyone on record and every receipt, with the fingerprint.
Open consentsNotice
Purposes in English, Hindi and Kannada, and three published versions.
Open noticeWebsite banner
Annapurna's homepage as a visitor sees it, with the consent banner.
Open website bannerConsent form
Yes or no to each purpose, in three languages; the receipt at the end.
Open consent formPrivacy page
An email code, then withdraw with a switch or make a request.
Open privacy pageNo password in the demo. The bar at the top switches company and person, opens the website as a visitor, or starts a company of your own.
Imran Sheikh
Data protection officer, Annapurna Organics
Everything but settings: requests, breaches, the notice and the data map.
Kavitha Rao
Owner (Founder)
Everything, plus settings, the team and the API key.
Deepa Nagaraj
Member (Customer support)
Consents and requests: the support desk's view. Breaches and the notice are read-only.
Ramesh Gowda
Administrative officer, Vidyanikethan Public School
A separate company: children's consents given by parents with an email code, and a request past its deadline.
Postgres runs in your tab and keeps your changes in this browser. Nobody receives email: codes show on the page and every email is in the outbox. “Reset demo” in the bar starts over.
On your own machine
npm installSEED_PASSWORD=choose-a-password npm run db:seednpm run devThen sign in with the sample admin:
Username
Password
choose-a-passwordOr whatever you set SEED_PASSWORD to. On Windows PowerShell: $env:SEED_PASSWORD="choose-a-password"; npm run db:seed
Without the seed, the first visit asks you to create your company. Name your privacy contact in Settings, add purposes and publish the notice, then paste the banner's script tag into your site.
Grouped by where the work happens.
Exact versions, because that is the first thing a developer checks.
consentdesk.zip, 200 KB: the whole project as it unzips, counted from the zip itself.
It gives you what the Act and Rules ask you to run and prove: a clear notice in the languages people read, consent that's specific and recorded, withdrawal as easy as consent, a way to exercise rights with answers inside the deadline, parental consent for children, a breach process with the 72-hour report, and records of your data and vendors. What you write in the notice, and how you use the data, is still yours to get right: have a lawyer read your notice before you publish it.
The DPDP Rules, 2025 were notified on 13 November 2025. Most of them, including the notice, consent, security, breach reporting, children's data and grievance redressal, apply from 13 May 2027.
Switch on “Children under 18 use our service”. The consent form then asks whether it's for the person or for their child; for a child, the parent or guardian gives their name and email and types a code sent to that email before anything is recorded. One parent can give consent for each child, and sees all of them on the privacy page.
On the privacy page: they type their email, enter the code sent to it, and switch any purpose off. That's a new receipt, emailed to them, and your other apps see it through the API. On your website, a “Cookie settings” link reopens the banner.
Every answer is stored as a receipt that's never changed: the code (like CD-7K2M-9Q4X), the notice version shown, each choice, the language, how it was given, the IP address and the time. The SHA-256 is a fingerprint of that content, so an emailed or printed copy can be checked against the record.
Yes. Make an API key in Settings; your CRM, HR or membership app can record consent from its own forms and check, before sending a message, whether the person agreed. The README has the two calls.
Ticket tracker
A team ticket tracker with subtasks, notes, watchers, linked tickets and the emails it sends.
Meeting scheduler
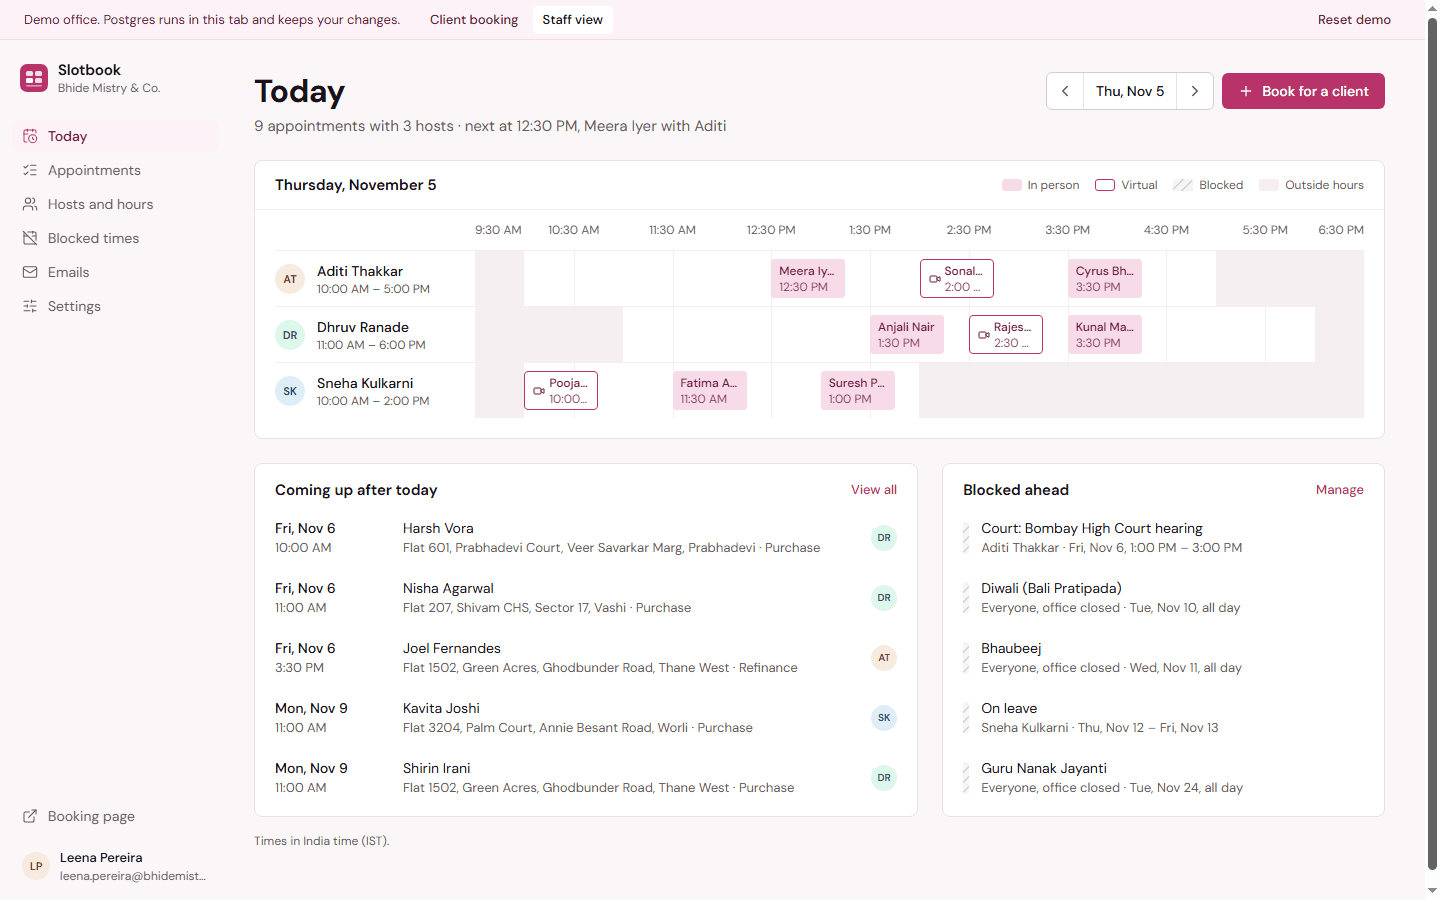
Clients pick a person, a day and a free time; staff see every host's day on one board.
Form builder
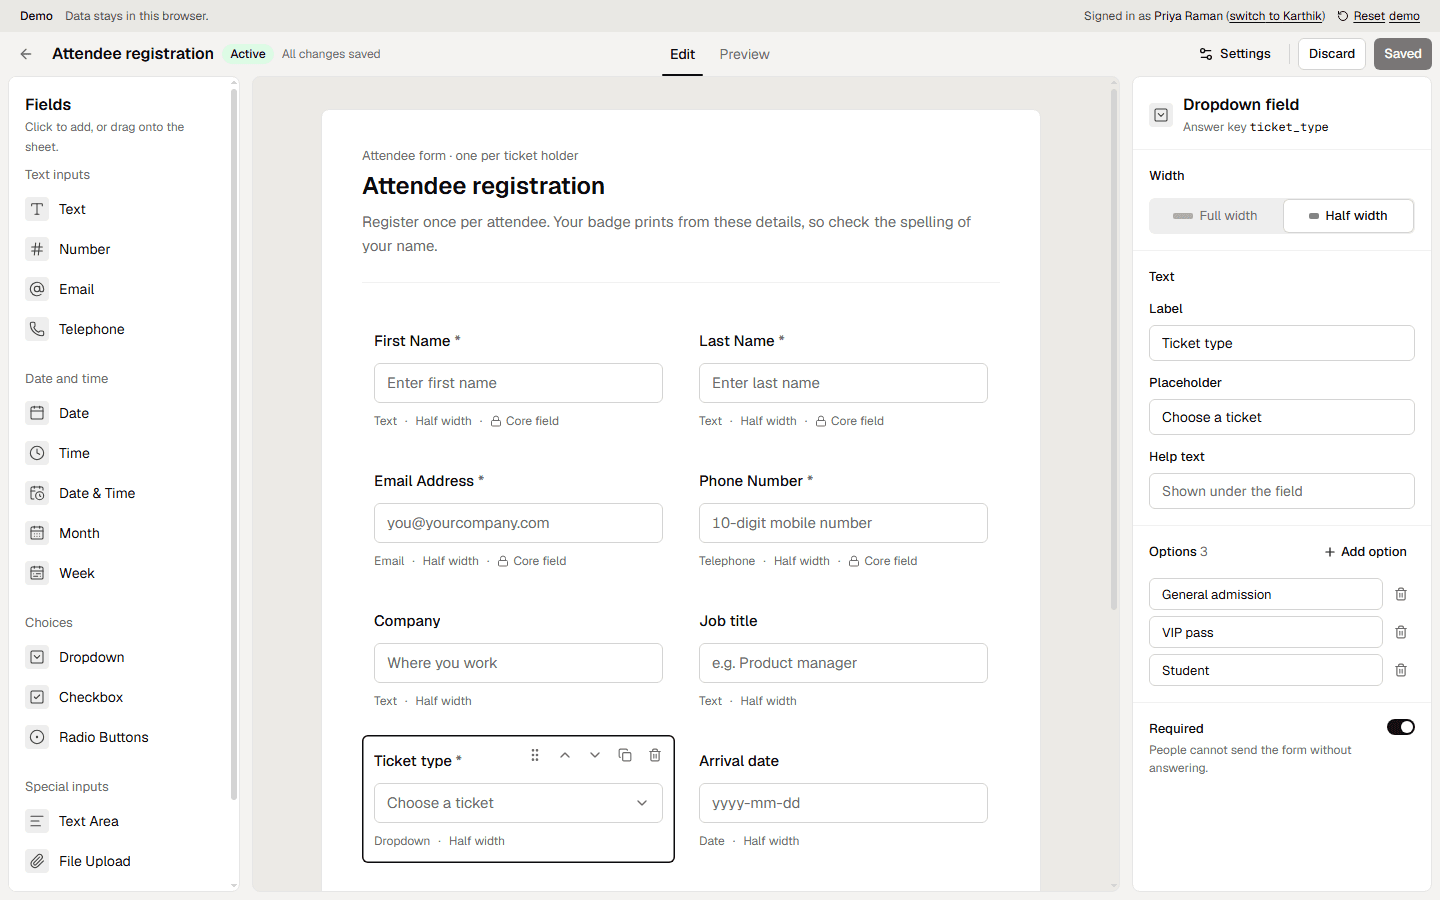
Build registration forms from a palette of fields, publish a link and read the responses.
Project chatbot
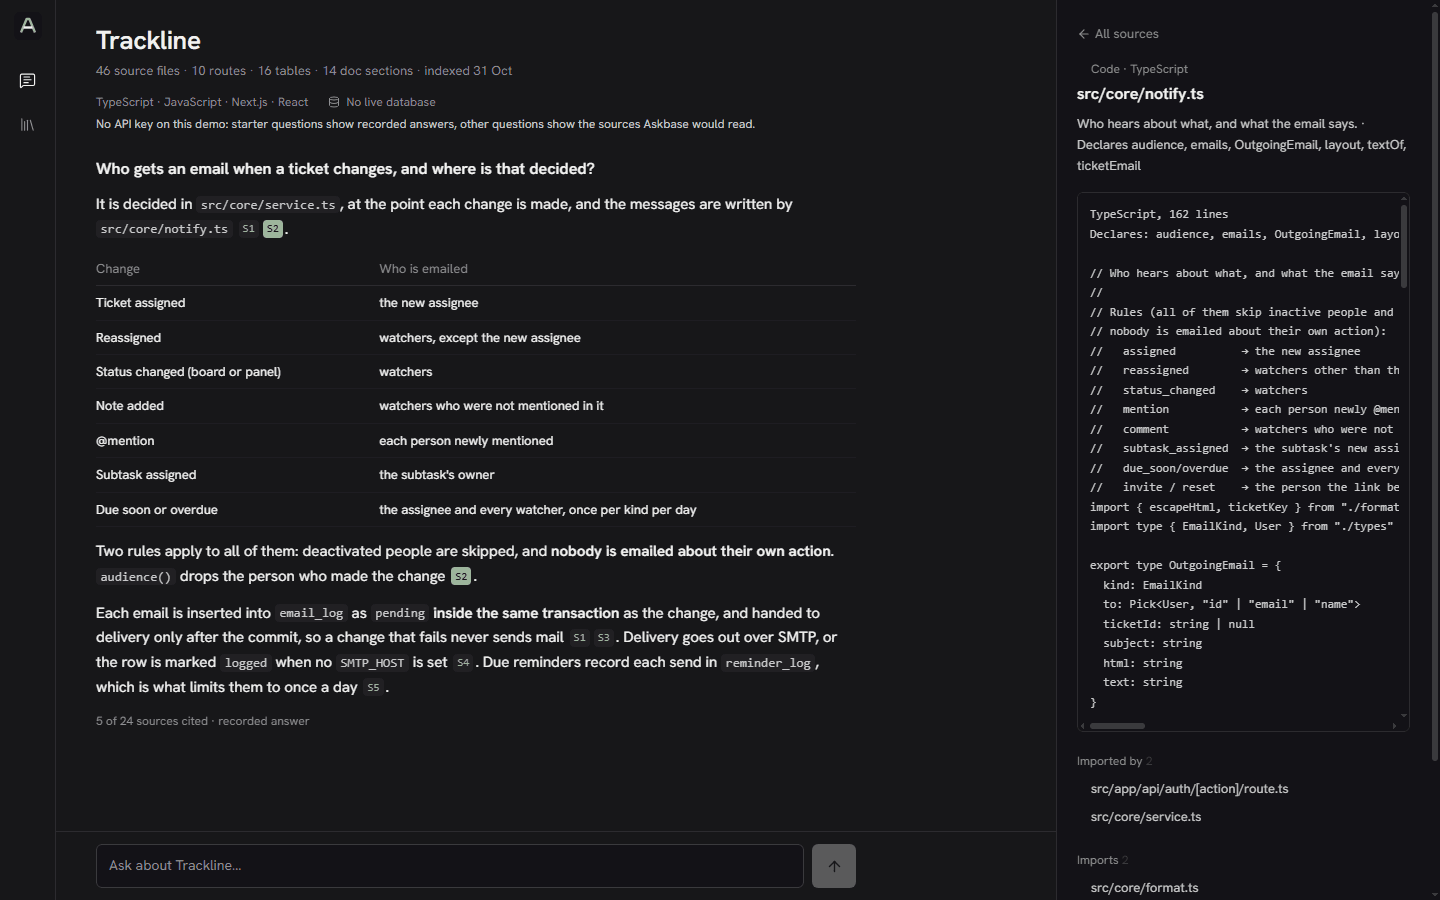
Ask any codebase how it works, and get answers that cite the files they came from.
KYC verification
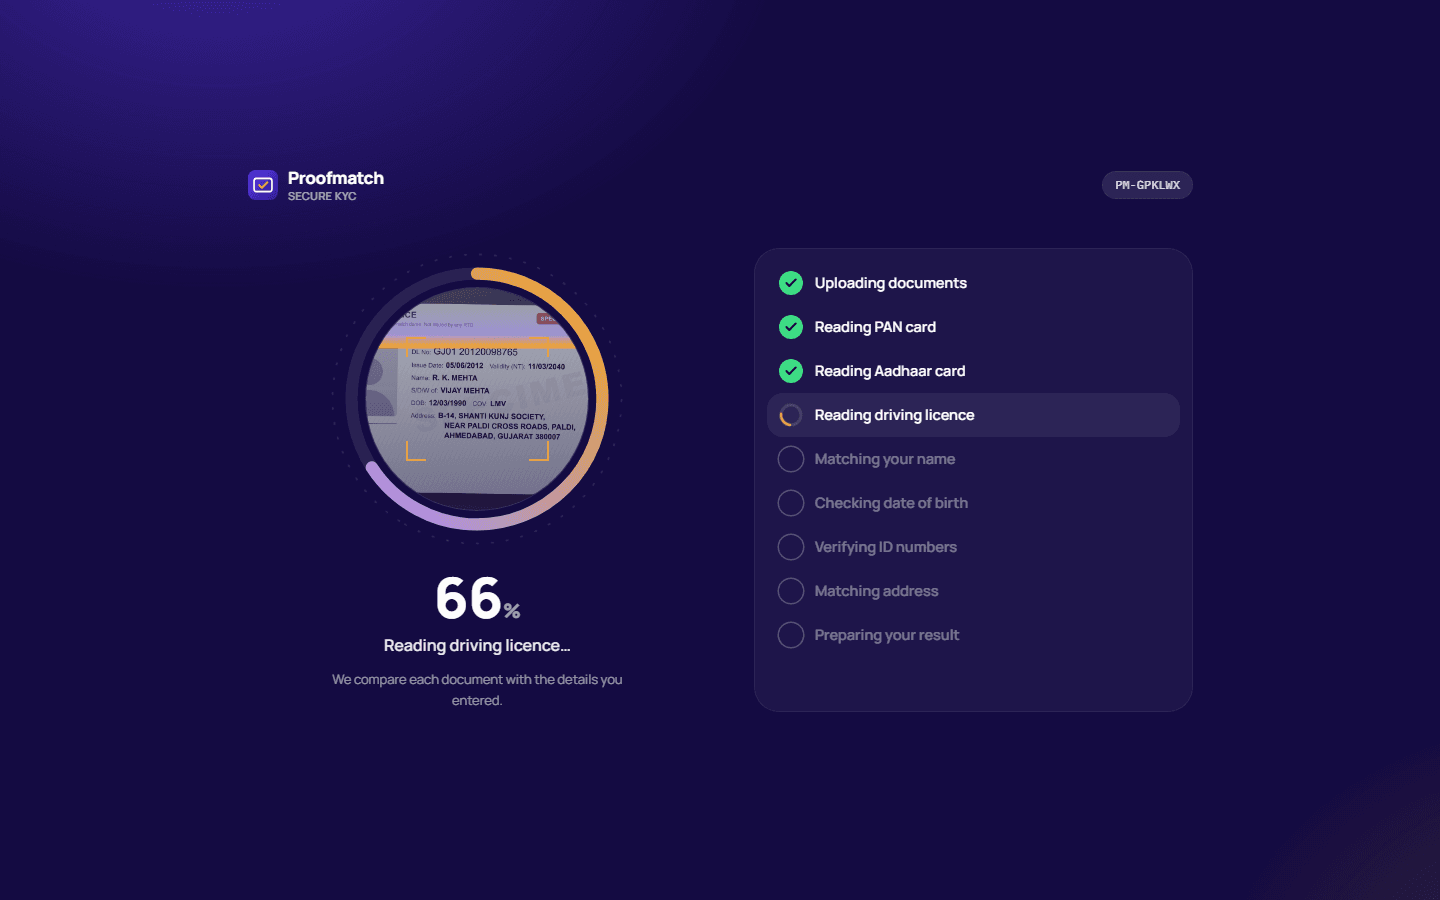
A KYC form for India that reads each PAN, Aadhaar and driving licence and checks it against what the applicant typed.
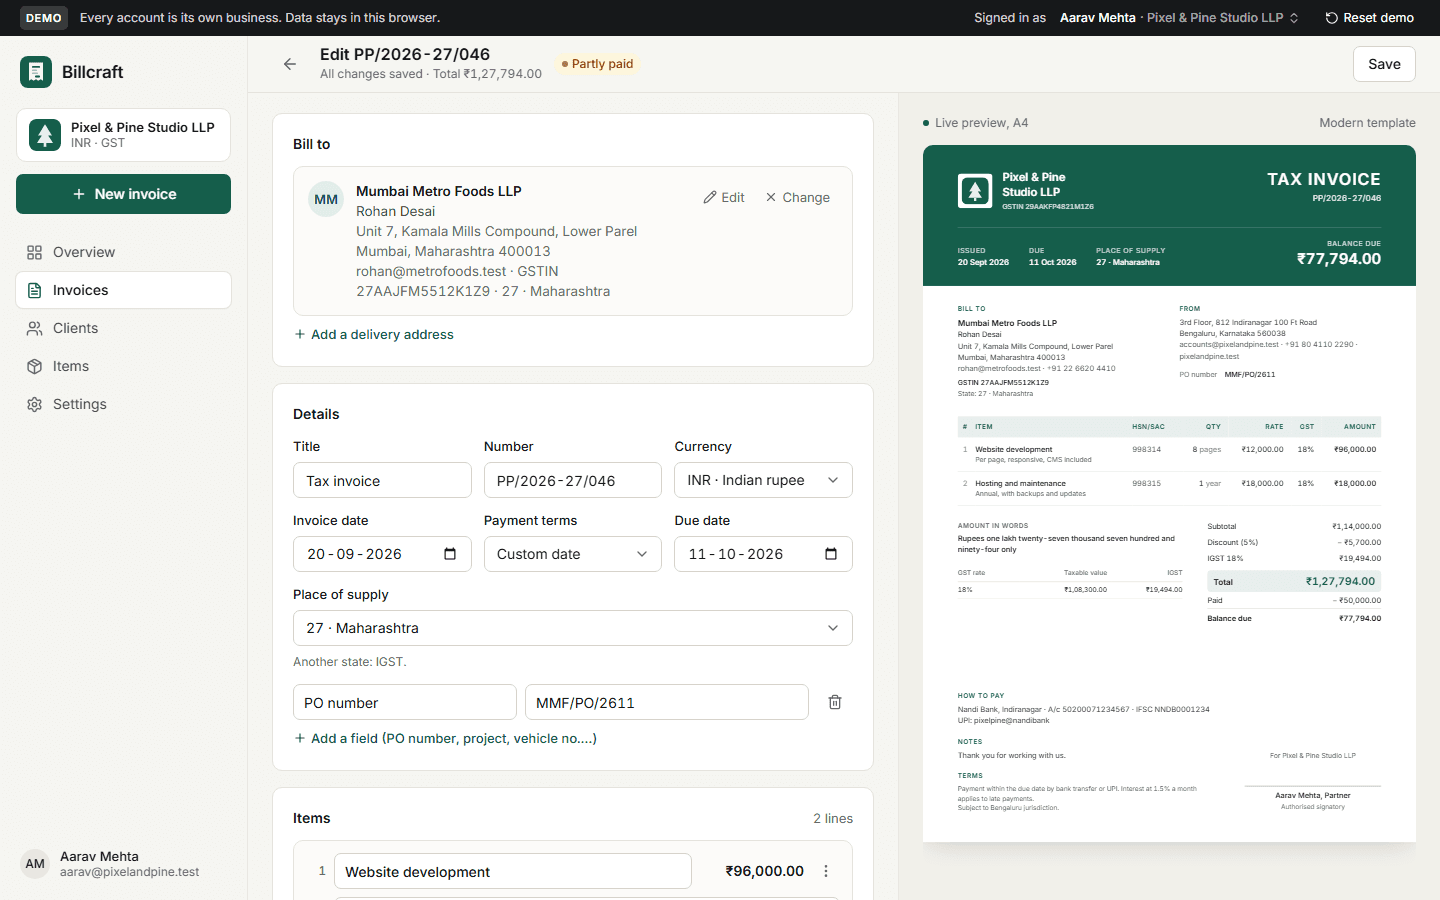
Invoice generator
GST invoices for any business: CGST + SGST or IGST, HSN/SAC, rupees in lakh and crore, three designs, a client link, payments and PDF.
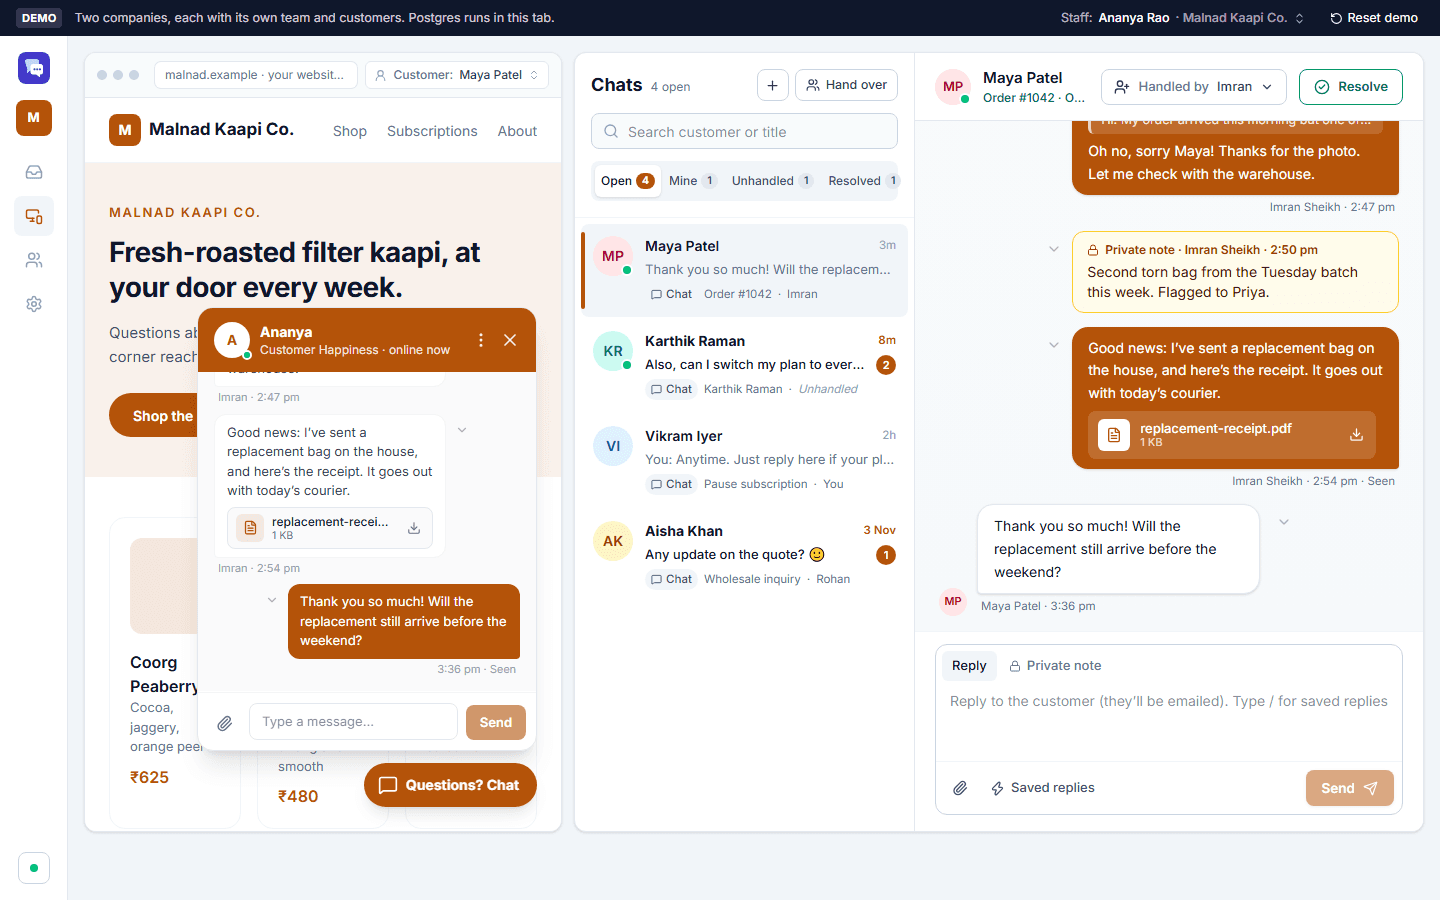
Live chat
Live chat for any number of companies: a chat button for each company's site and a shared inbox for its team.
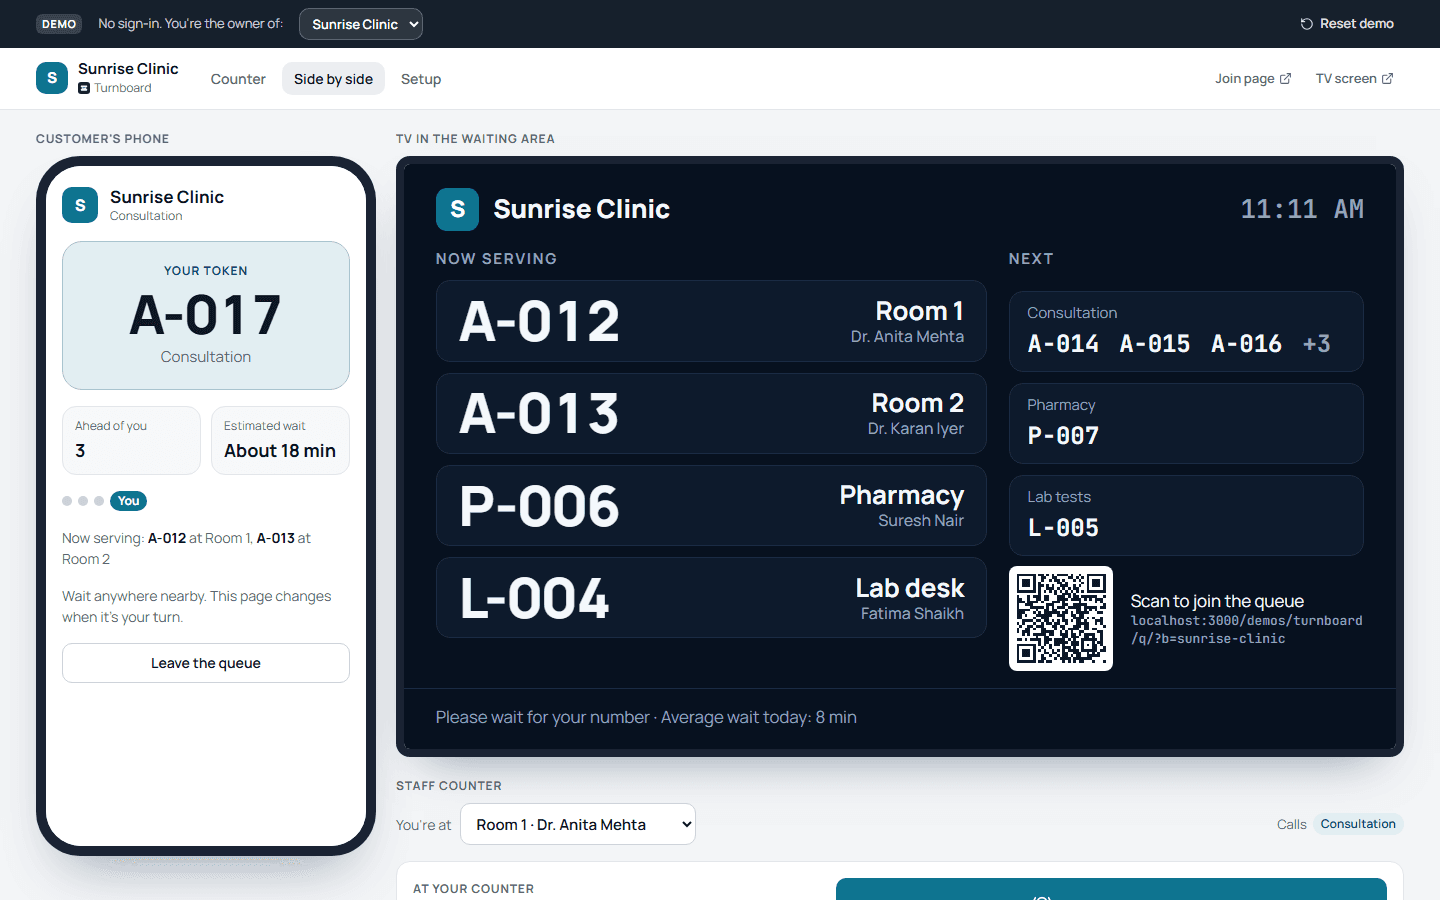
Walk-in queue
A walk-in queue: customers take a token on their phone, staff call the next person with one tap, and a TV shows who is being served where.
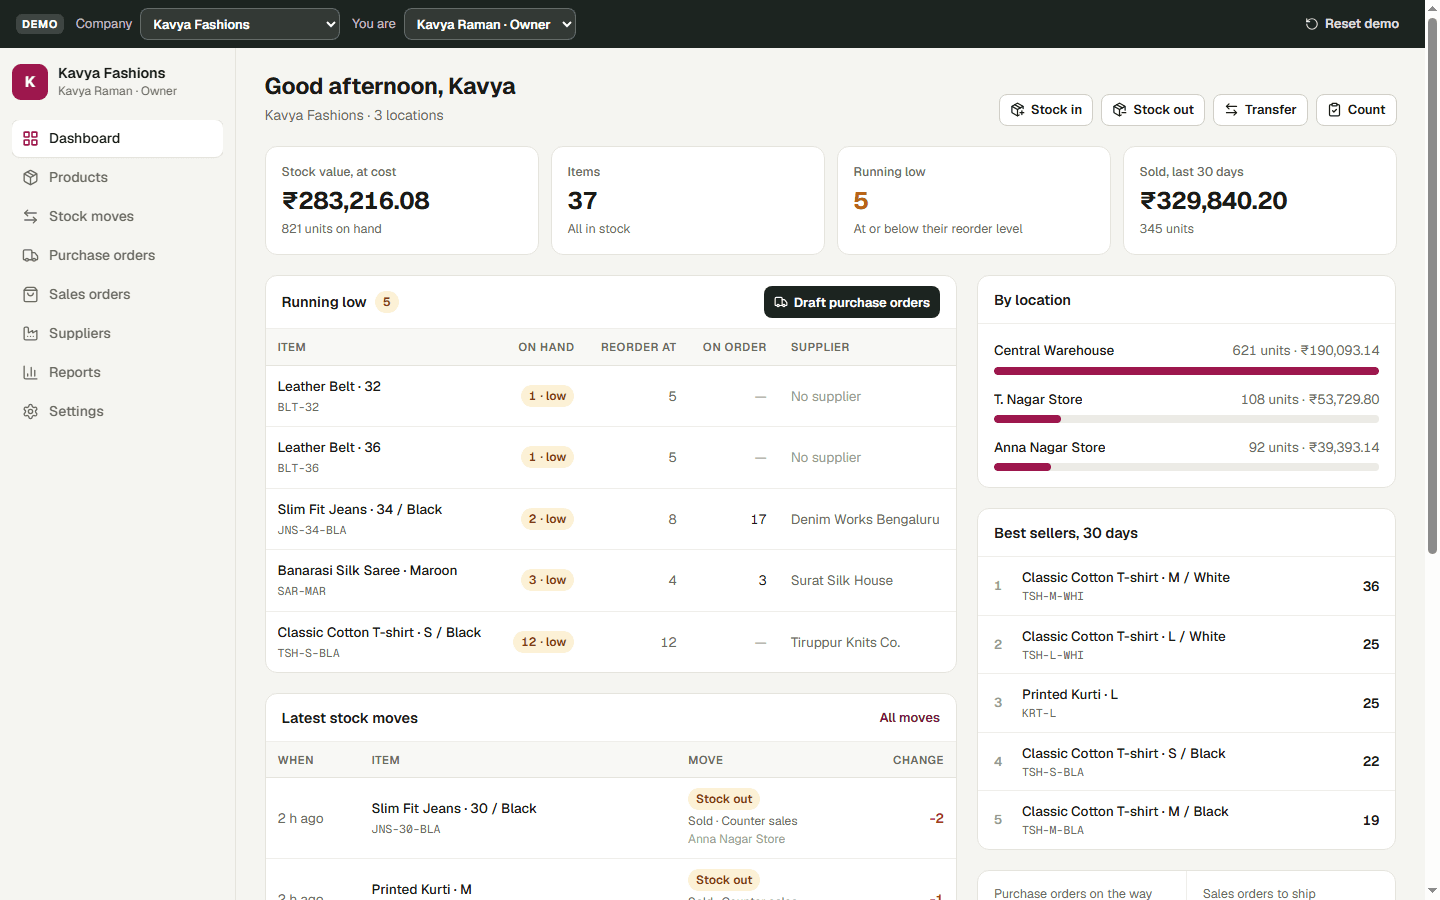
Inventory and stock
Inventory for any number of companies: products with variants, several warehouses and shops, stock moves with full history, reorders, purchase and sales orders, and reports.
Recruitment and applicant tracking
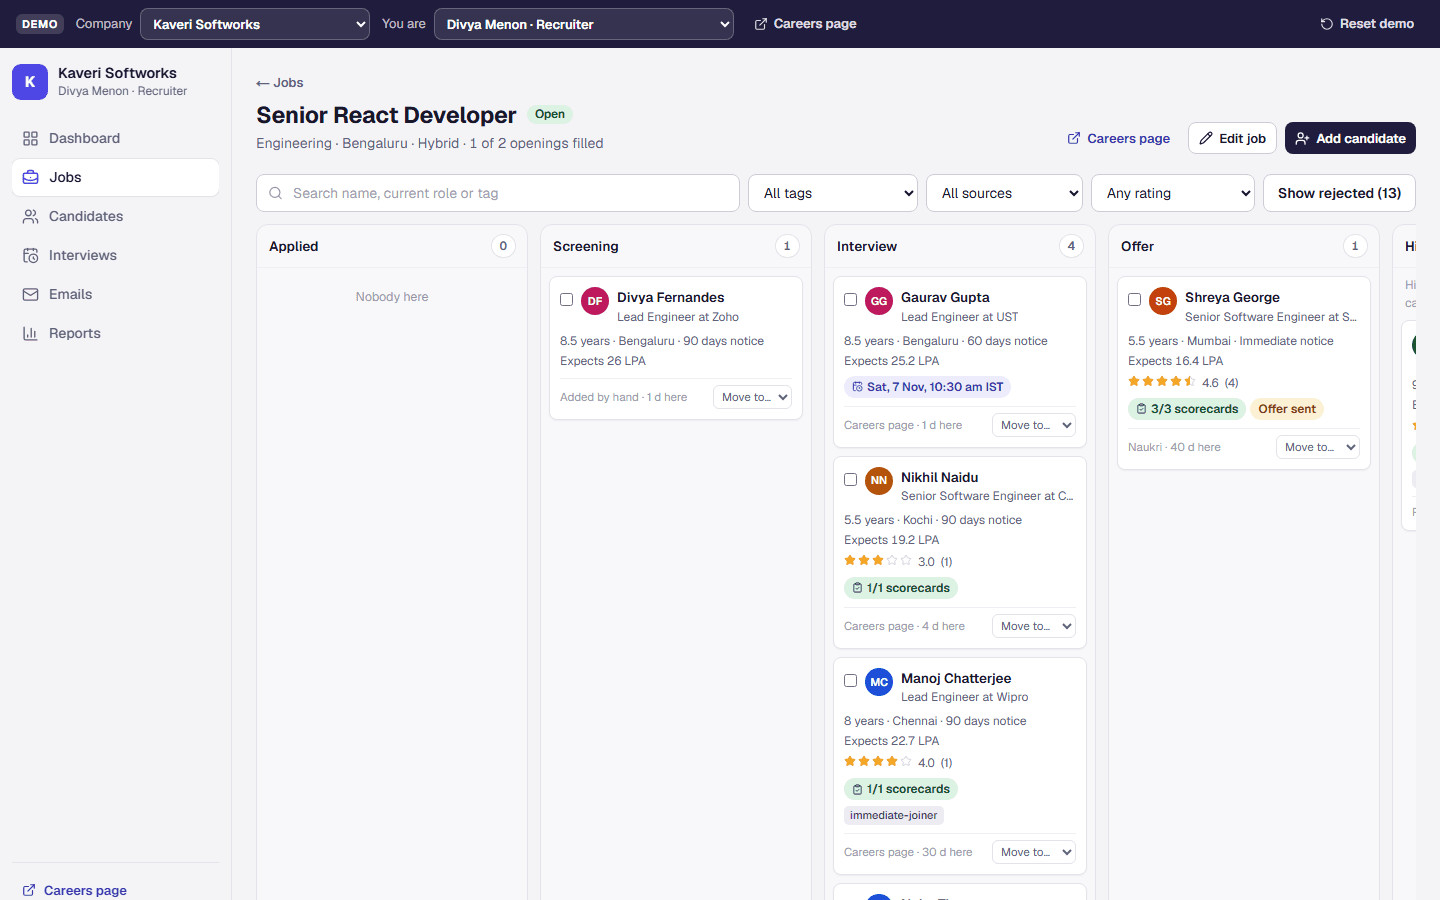
Hiring for any number of companies: jobs, a careers page with CV upload, a drag-and-drop pipeline, interviews with scorecards, emails, and offers with a CTC breakdown.
Sales CRM
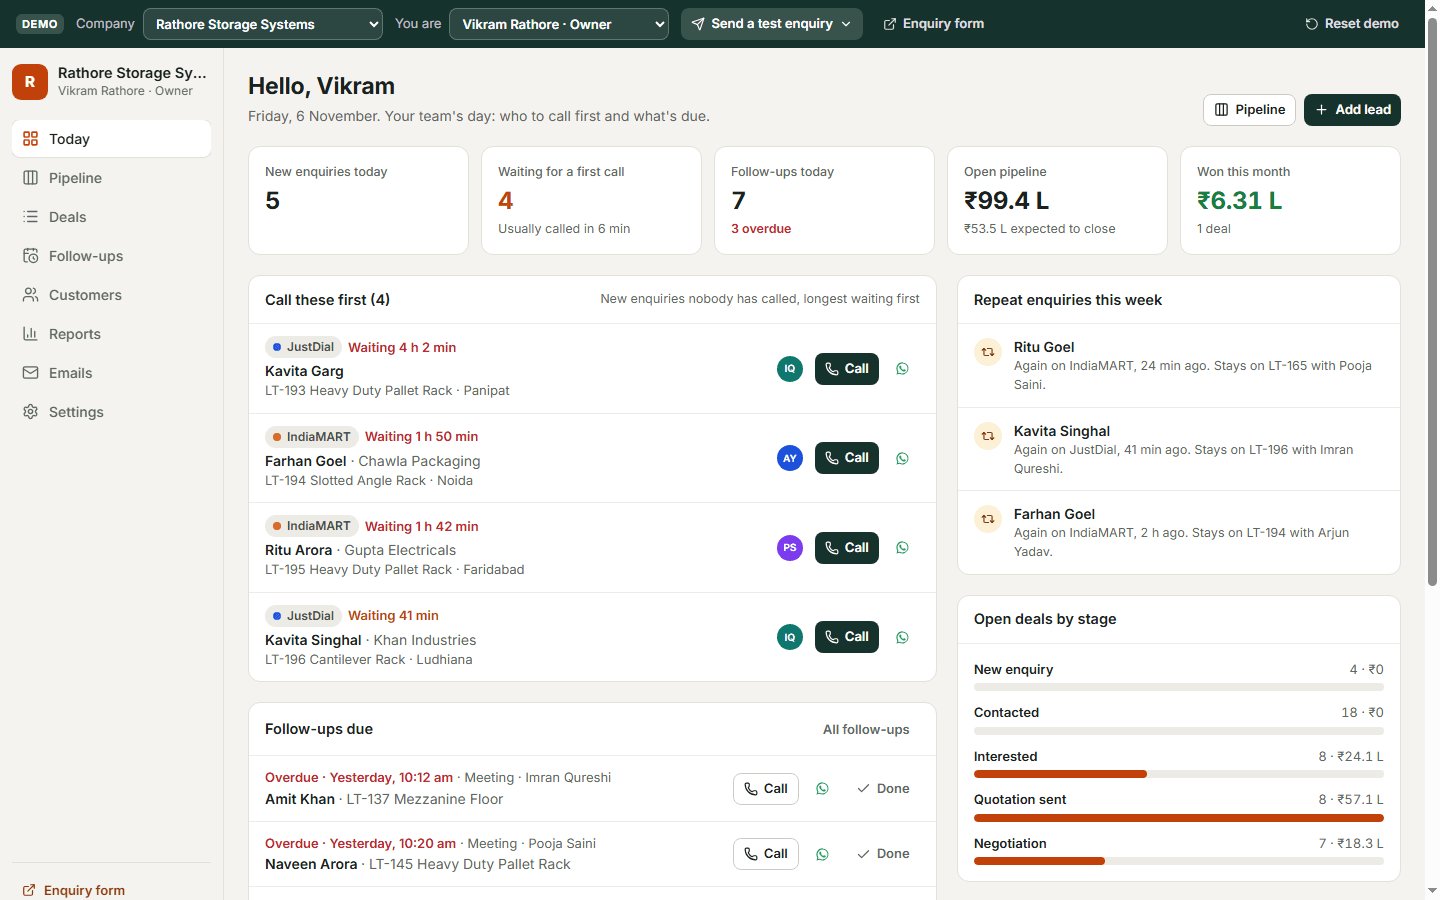
A sales CRM for any number of companies: enquiries from IndiaMART, JustDial, Facebook and the website, a repeat check on every mobile number, follow-ups, WhatsApp templates, a drag-and-drop pipeline, and one-click invoices in Billcraft.
E-signature
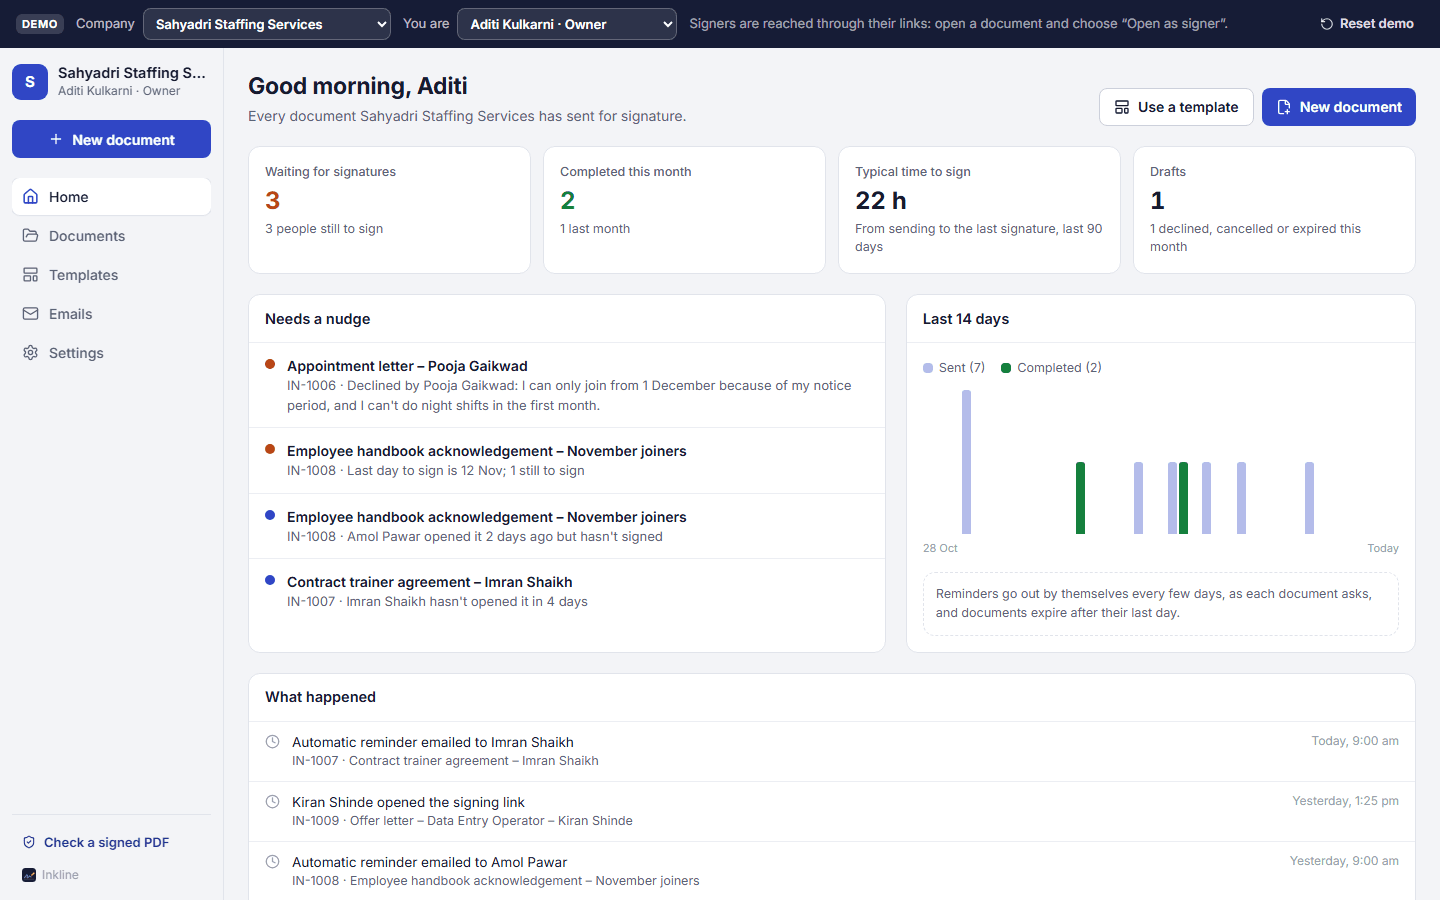
E-signature for any number of companies: upload a PDF, place signature boxes, send a link; each person signs on their phone after a one-time code, and everyone gets the signed PDF with a certificate of who signed, when and from where.
Membership management
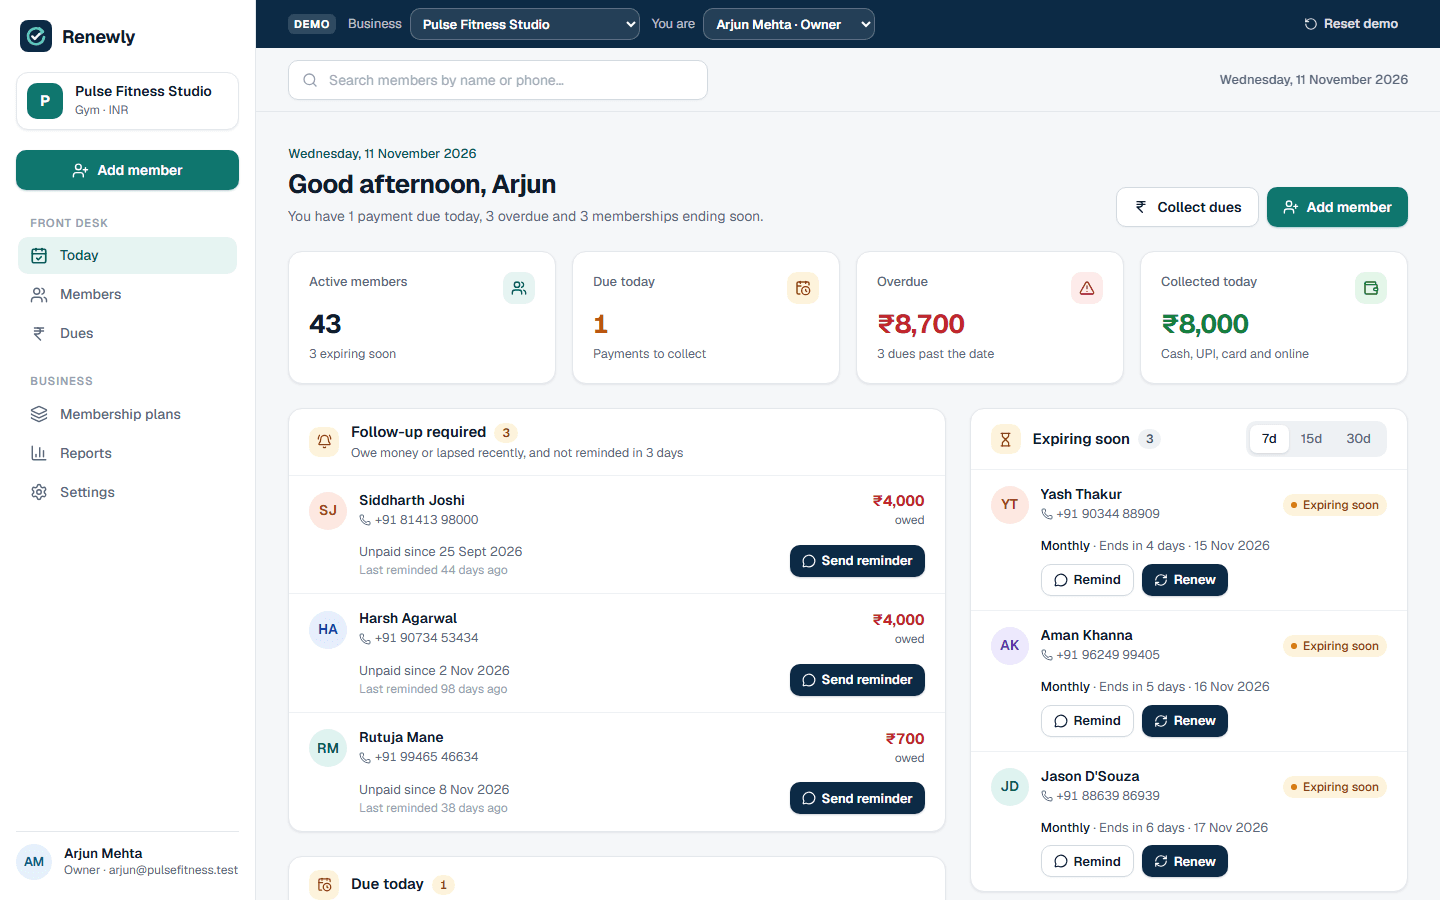
Memberships and fees for gyms, studios, dance academies and coaching classes: members and plans, part payments with receipts, renewals and pauses, WhatsApp reminders, Razorpay payment links, and a Today screen of who to collect from and who to renew.